
Phishing scams target tourists after RMS booking data breach
Travelers to Broome received fraudulent messages that referenced real reservation details, prompting warnings from hotels and a cybersecurity expert.
Travelers to Broome received fraudulent messages that referenced real reservation details, prompting warnings from hotels and a cybersecurity expert.
The story
A data breach involving Australian third‑party accommodation booking provider RMS has led to a wave of phishing scams aimed at travellers planning visits to the Kimberley region of Western Australia. Hackers accessed personal information, including names, booking dates and contact details, from RMS’s database and used the data to craft messages that appeared to come from legitimate hotels.
One affected traveller, Cameron Craig of Sydney, reported receiving a WhatsApp message that referenced his upcoming stay at Cable Beach Club in Broome. The message asked him to confirm payment details via a link, warning that his reservation would be cancelled otherwise. Craig entered some credit‑card information before the session timed out and later recognised the sender as an international number with an incorrect reservation code.
Cable Beach Club confirmed that it had been alerted to the fraudulent communication and subsequently warned other guests about the scam. RMS said investigations were ongoing to determine the full extent of the breach and its impact on customers nationwide. The company has not disclosed how many individuals’ data were compromised.
A closer look
Cybersecurity experts described the scheme as “weaponising urgency,” noting that the inclusion of accurate booking information makes the scams more convincing. They advised travellers to verify any payment requests directly with the accommodation provider and to avoid clicking links in unsolicited messages.
Authorities have urged anyone who received similar messages to report them to their financial institution and to the Australian Cyber Security Centre. The incident highlights the broader risk of data breaches in the tourism sector and the need for robust security measures by booking platforms.
This report presents the named publisher’s account and has not yet been independently corroborated.
Continue reading
Australia desk ↗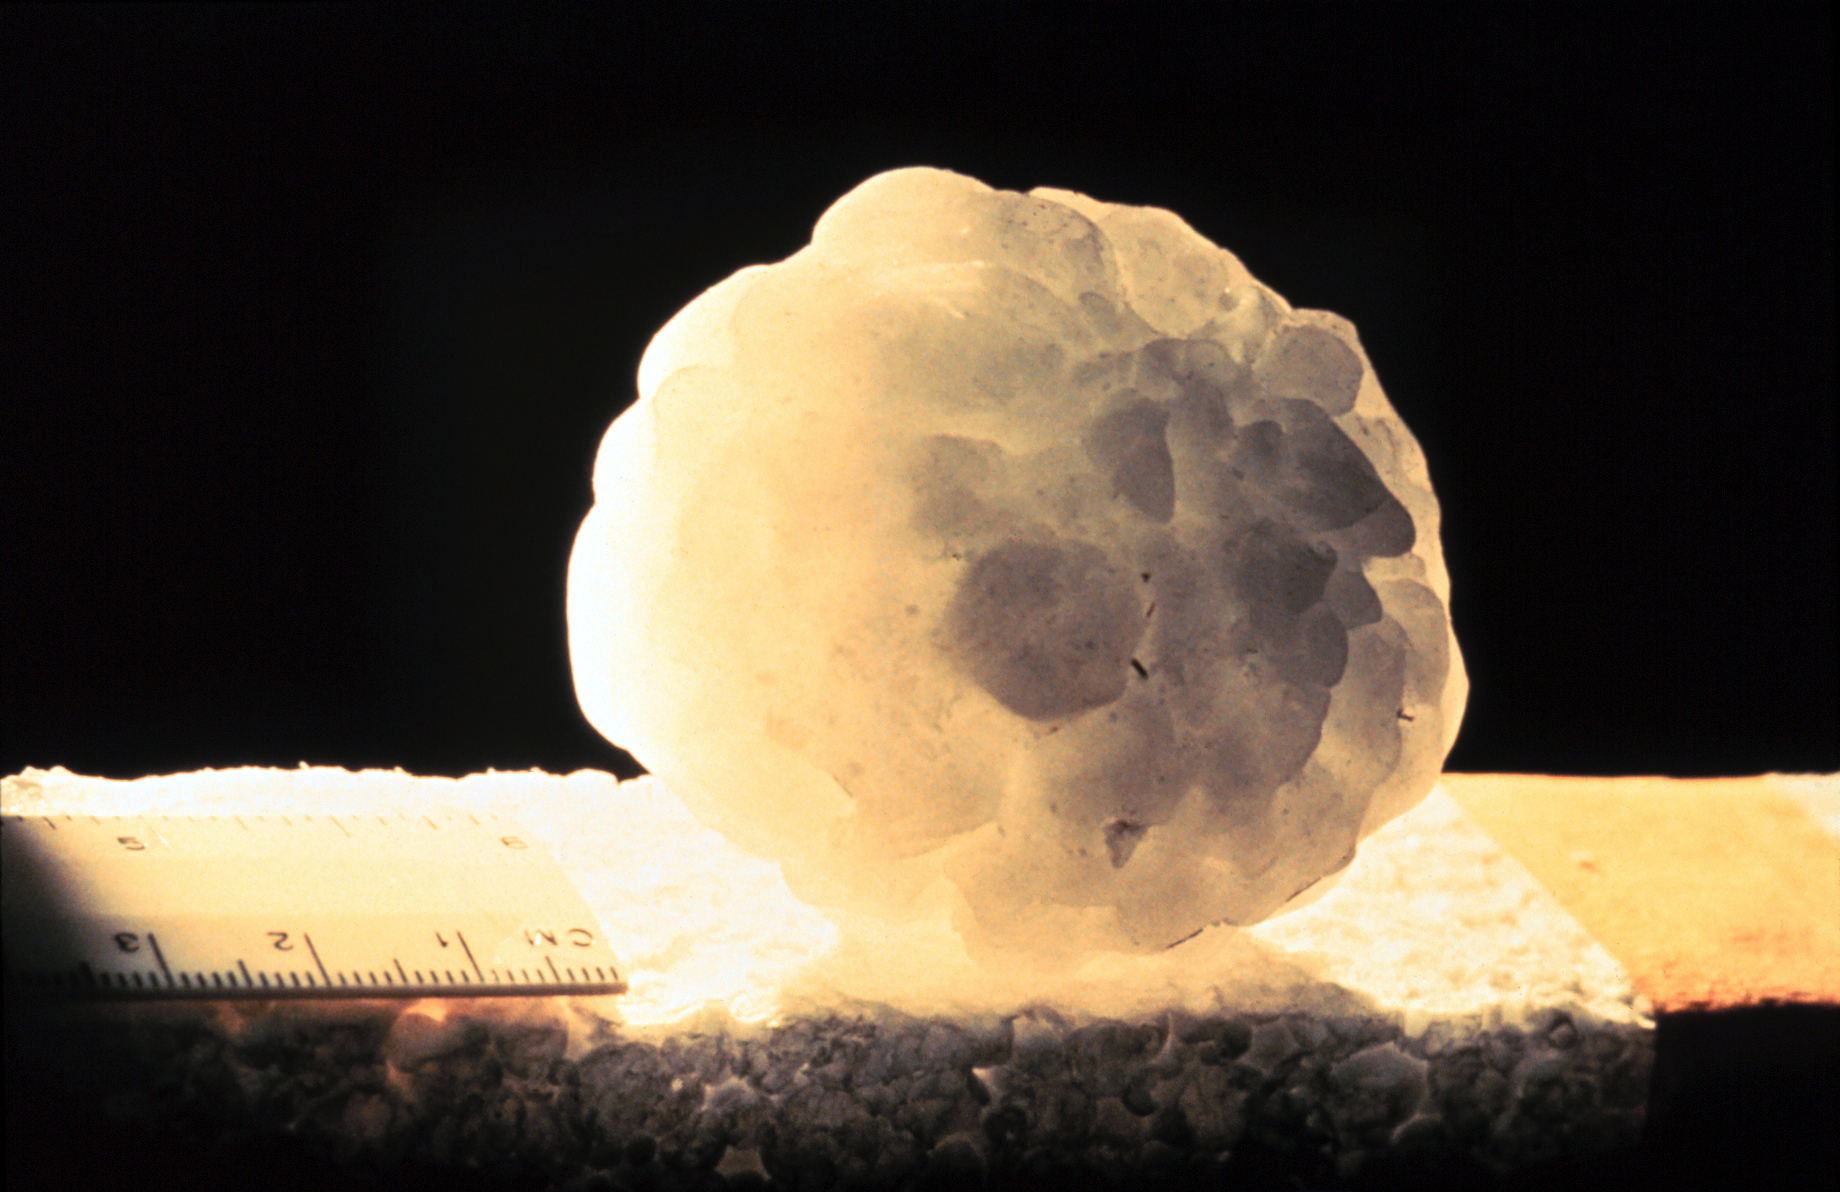
Severe Storms and Supercells Forecast for Parts of Queensland and New South Wales
The Bureau of Meteorology warns of potential destructive winds, giant hail, and heavy rainfall following overnight storms on the Fraser Coast.
Lower Eyre Council Removes Mandatory Acknowledgement of Country
A South Australian local government body has voted to eliminate its required Acknowledgement of Country, prompting disappointment from First Nations residents and varying perspectives from elected members.
Brisbane nurse charged with multiple rapes of elderly patients faces committal hearing
Jeremy David Pearce, 42, is accused of raping three women aged over 70 while employed at Greenslopes Private Hospital between 2020 and 2024; one alleged victim has died.